Full-stack engineer, hardening into application security.
Several years building production web apps — now going deep on AppSec: SAST/SCA tooling, secure pipelines, and cloud security fundamentals, through hands-on projects rather than theory alone.
Skills
AppSec & Security Tooling
Cloud & DevSecOps
Full-Stack & Frontend
Journey
Where I want to be
19 years in software engineering, now focused on Application Security and DevSecOps: hands-on with SAST, DAST, SCA, secrets and container scanning, CI/CD security gates, SIEM-based findings centralisation and STRIDE threat modelling, with production experience triaging and remediating vulnerabilities at scale. Seeking a dedicated Application Security / Product Security / DevSecOps role.
Projects
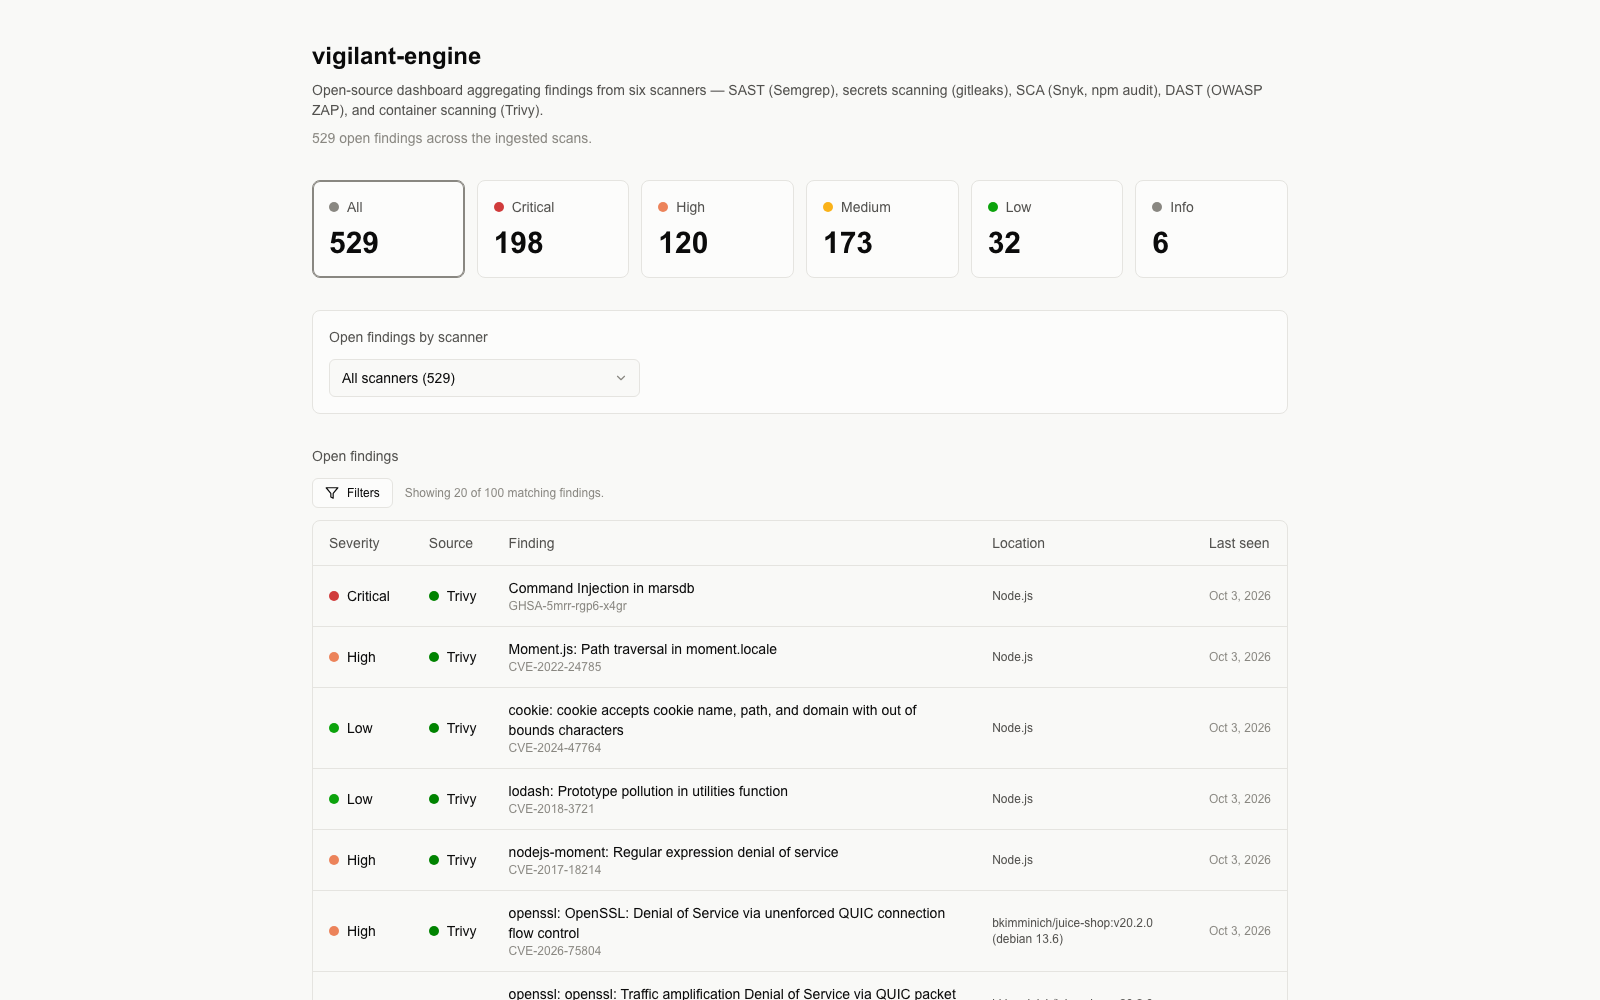
An AppSec & DevSecOps findings pipeline: six scanners (Semgrep, npm audit, Snyk, gitleaks, OWASP ZAP, Trivy) run against OWASP Juice Shop on every push via GitHub Actions, results normalize into one schema, and a Next.js dashboard surfaces what needs fixing.
Authored a STRIDE-based threat model, then wired SAST, DAST, SCA, secrets and container scanning into CI — surfacing 529 open findings (198 critical, 120 high), manually verified with Burp Suite. Deployed on AWS with the dashboard on Vercel and a Postgres database.
View on GitHub →Tenant-isolation-as-code: a FastAPI demo with a reusable authz layer enforcing row-level tenant scoping, plus a fuzzer that attacks every route for cross-tenant IDOR and fails CI on leaks.
View on GitHub →A Python cloud-config auditing toolkit: checks S3 buckets and security groups against security baselines and reports findings in a common schema, with CI running pytest, bandit and pip-audit.
View on GitHub →Articles
What SAST actually catches (and what it misses)
Building vigilant-engine: normalizing three scanners into one schema
Frontend engineer's field notes on AppSec
Feed wires up to Medium once the first article publishes.